



SOC 2 Risk Assessment & Vendor Management Kit
SOC 2 Risk Assessment & Vendor Management Kit
Regular price
$49.00 USD
Regular price
Sale price
$49.00 USD
Instant download. Editable files. One-organization licence. 5-day fit guarantee.
Couldn't load pickup availability
Upgrade and save
This is one of the 3 kits in the SOC 2 Starter Bundle: 20 policy templates, the readiness assessment and control matrix, and the risk assessment and vendor management kit. Get all 3 for $199 instead of $237 bought separately.
See the SOC 2 Starter Bundle (Policies, Control Matrix, Risk & Vendor)Want everything for the audit? The SOC 2 Compliance Toolkit has all 52 templates for $249.
Not ready to buy? Get the free SOC 2 readiness checklist
5-day fit guarantee. If it does not fit your SOC 2 program, ask for a refund within 5 days. Conditions.
A credible SOC 2 risk assessment and vendor management program without buying a GRC platform. These are two areas where first-time SOC 2 companies often have thin evidence.
What you get
- Risk Assessment Procedure (Word, 6 pages): a step-by-step method for the annual and change-driven risk assessment, including fraud risk (CC3.1 to CC3.4), with a fictional worked example.
- Risk Register (Excel): a 5 x 5 register with 47 pre-written SaaS risks written as cause, event and consequence, inherent and residual scoring, an appetite flag, heat maps and a dashboard.
- Vendor Management Procedure (Word, 6 pages): intake, tiering, due diligence by tier, how to review a SOC 2 report and its complementary user entity controls (CUECs), contract terms, monitoring and offboarding (CC9.2).
- Vendor Inventory and Risk Tiering (Excel): automatic tiering from six questions, review due dates, a 14-step SOC report review checklist, review log, CUEC mapping and dashboard.
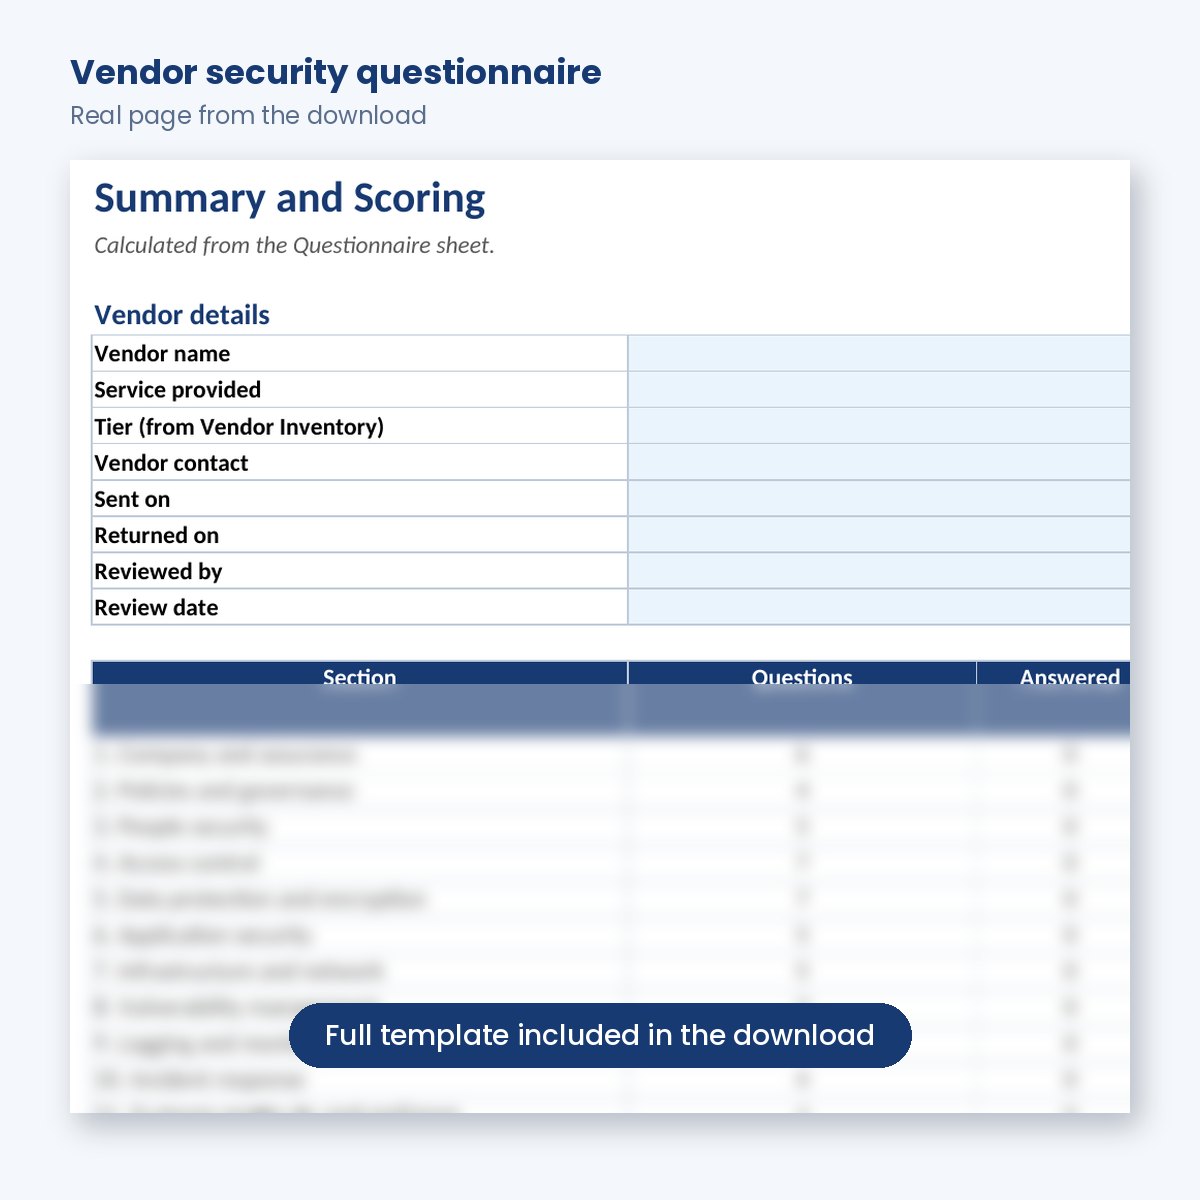
- Vendor Security Questionnaire (Excel): 62 questions in 14 sections with answer dropdowns, weights, critical flags and automatic scoring.
- Start Here guide (PDF): the order of work, what good looks like and common mistakes.
Also included in the SOC 2 Starter Bundle and the SOC 2 Compliance Toolkit.
How to use it
- Read the procedure and confirm scales and appetite with the CEO.
- Adapt the example risks, then run a 60 to 90 minute workshop with your leads, including a fraud discussion.
- Agree treatments, get CEO approval and save a dated copy as evidence.
- List every vendor (check your identity provider app list, expense reports and cloud marketplace) and let the workbook tier them.
- Review SOC reports from Critical and High vendors, map the CUECs, and send the questionnaire to vendors without a report.
Who it is for
The person responsible for SOC 2 readiness at a SaaS company, and teams whose platform's built-in risk register feels generic. Auditors want to see real risks, fraud discussed, risk reviewed when things change, and vendor SOC reports actually read.
Good to know
- Instant download. Editable Word (.docx) and Excel (.xlsx), plus a PDF guide. Works in Excel 2016 or later, Microsoft 365 and LibreOffice; no macros.
- Licensed for use within one organization.
- Criteria are referenced by number and summarized in our own words; the AICPA criteria are free to download from the AICPA.
- SOC 2 is an attestation report by a licensed CPA firm, not a certification. These templates help you prepare; they do not guarantee an unqualified SOC 2 opinion.
- 5-day fit guarantee: if it does not fit your system, contact us within 5 days of purchase.


What every download includes
Instant downloadLink on the confirmation page and by email within minutes.
Fully editableWord (.docx), Excel (.xlsx) and PDF. No macros. Works in Microsoft 365 and Google Workspace.
5-day fit guaranteeIf the files do not fit your SOC 2 program, ask for a refund within 5 days. Conditions apply.
Free updatesRevised files for the current version of the Trust Services Criteria are sent to you at no charge. One-organization licence.
Templates refer to Trust Services Criteria numbers (for example CC6.1) and describe them in our own words; they do not reproduce AICPA text. A SOC 2 report is issued by a licensed CPA firm. Templates help you prepare; they do not guarantee a clean report.
Questions about SOC 2 Risk Assessment & Vendor Management Kit
Why do SOC 2 auditors focus on risk assessment and vendors?
The common criteria require you to set objectives, identify and analyze risk including fraud, and assess risk when things change (CC3.1 to CC3.4), and to manage vendor and partner risk (CC9.2). First-time companies often have thin evidence here, so auditors look closely at the register, workshop minutes, vendor inventory and SOC report reviews.
Can we just use the 47 example risks?
Use them as a starting point, not as your assessment. Delete what does not apply, adapt the wording, assign owners and re-rate each risk in a workshop. Auditors ask how ratings were decided, and copied ratings without discussion are easy to spot. Rating everything High also stops the register helping you prioritize.
What are CUECs and why do they matter?
Complementary user entity controls are the controls a vendor's SOC report expects you, the customer, to operate, such as managing your own users in their system. If you ignore them, the vendor's report may not cover the risk you rely on it for. The kit's CUEC mapping sheet records each one and who owns it.
When should we send the vendor questionnaire?
Send it to vendors that do not have a SOC 2 report, or where the report does not cover the service you use. It has 62 questions in 14 sections, with weights and critical flags, so a score and any critical failures appear automatically. Allow about an hour to review each response.
How will I receive the files?
A download button appears on the order confirmation page and the same link is emailed to you within a few minutes. Bundles arrive as one ZIP file.
Can I get a refund?
Yes. With our 5-day fit guarantee, if the files do not fit your SOC 2 program you can ask for a full refund within 5 days of your order. It applies once per customer and organization, covers the whole product, and requires you to confirm you have deleted the files. We also refund non-delivery, defective files, wrong items and duplicate purchases within 30 days. Read the full refund policy.
Can I see the files before I buy?
Yes. The images above show real pages from the files, and the free SOC 2 readiness checklist lets you check where you stand before you buy.
Can I use the templates with more than one company?
Each purchase is licensed to one organization. Consultants and groups need one licence per client or legal entity. See the licence agreement.
Templates that work with this one
Useful next steps when you prepare for a SOC 2 audit.

