



NIST 800-171 System Security Plan (SSP) Template
NIST 800-171 System Security Plan (SSP) Template
Regular price
$99.00 USD
Regular price
Sale price
$99.00 USD
Instant download. Editable files. One-organization licence. 5-day fit guarantee.
Couldn't load pickup availability
Upgrade and save
This is one of the 3 tools in the CMMC Level 2 Starter Bundle: the NIST 800-171 assessment workbook with SPRS calculator, the System Security Plan template and the POA&M tracker. Get all 3 for $175 instead of $207 bought separately.
See the CMMC Level 2 Starter Bundle (Workbook, SSP, POA&M)Need the policies and procedures too? The CMMC Level 2 Compliance Toolkit has all 32 templates for $279.
Not ready to buy? Get the free CMMC Level 1 self-assessment checklist
5-day fit guarantee. If it does not fit your CMMC program, ask for a refund within 5 days. Conditions.
A complete System Security Plan template for NIST SP 800-171 and CMMC Level 2, with an example statement for every requirement. An SSP is required by requirement 3.12.4; without one, your self-assessment cannot be scored.
What you get
- System Security Plan Template (Word, 81 pages): system identification, scope and boundary using the CMMC asset categories, environment, network and data flow diagrams, external providers and shared responsibility, roles, and all 110 requirements with verbatim NIST text, their 320 assessment objectives, status boxes and a fictional example implementation statement for each. Appendices include a change log.
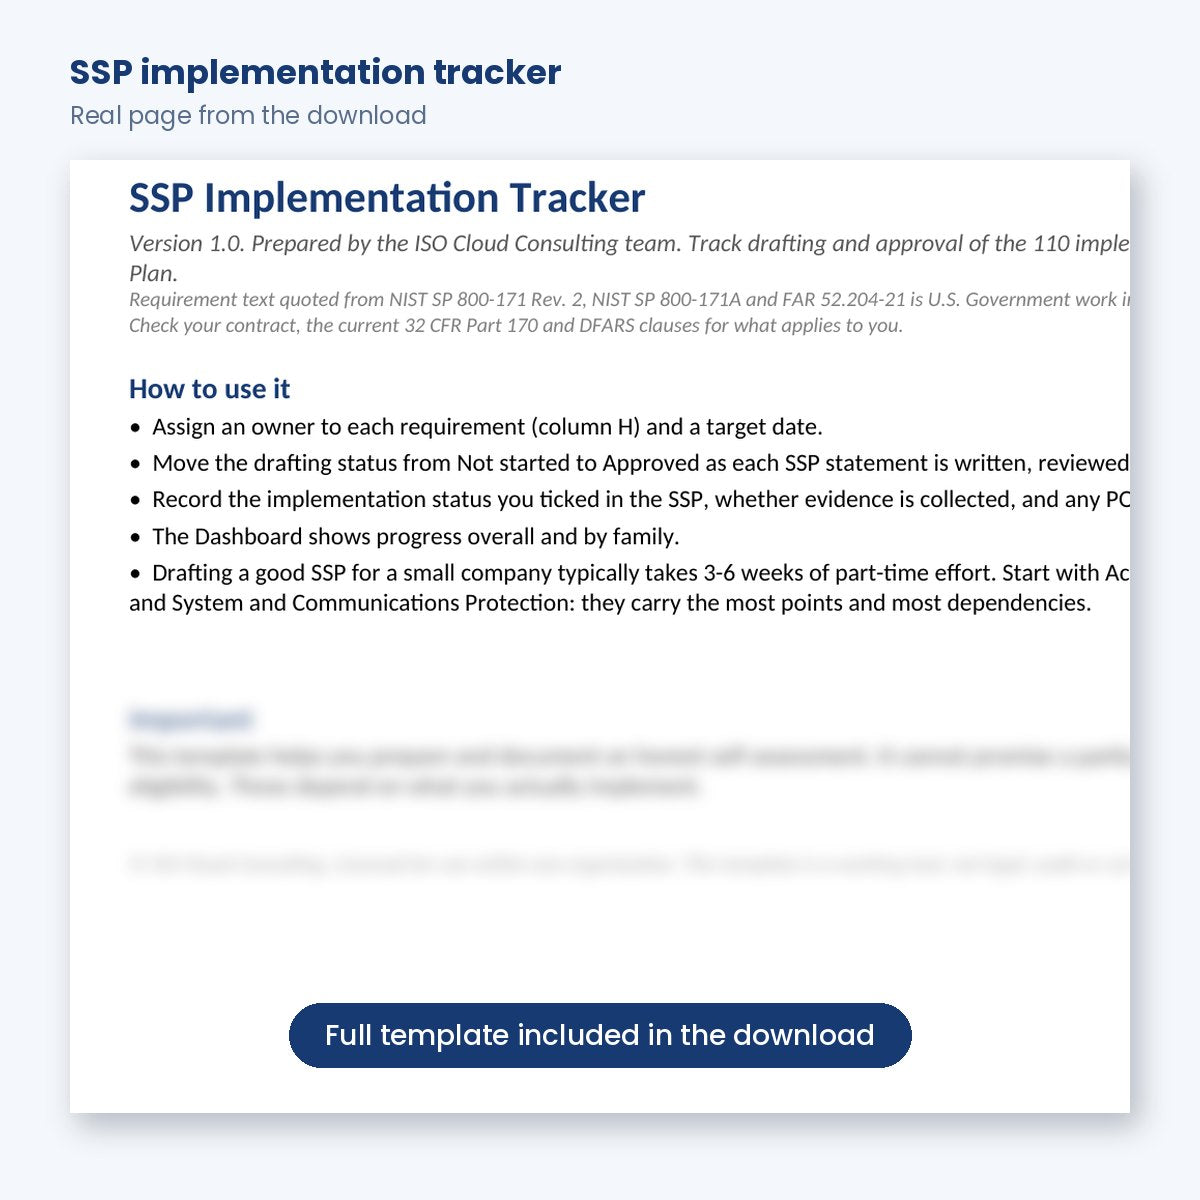
- SSP Implementation Tracker (Excel): a 110-row tracker for drafting, review and approval of each statement, with owners, target dates and a dashboard by family.
- Start Here guide (PDF): steps, what good looks like and common mistakes.
Also included in the CMMC Level 2 Starter Bundle and the CMMC Level 2 Compliance Toolkit.
How to use it
- Complete sections 1 to 3 (identification, scope and boundary, roles) and draw the diagrams (1 to 3 days).
- Assign an owner and target date to each requirement in the tracker (1 hour).
- Draft section 4 family by family, starting with Access Control, Identification and Authentication, and System and Communications Protection. Replace every blue example with your own statement (3 to 6 weeks part time).
- Review each statement against its objectives and evidence, and record gaps on your POA&M.
- Approve the SSP, use it for your self-assessment and SPRS entry, and review it annually.
Who it is for
Small and mid-sized defense suppliers that handle CUI (Controlled Unclassified Information) and need an SSP for a NIST SP 800-171 or CMMC Level 2 self-assessment, and the MSPs who write SSPs for them.
Good to know
- Instant download. Editable Word (.docx) and Excel (.xlsx), plus a PDF guide. Works in Excel 2016 or later, Microsoft 365 and LibreOffice; no macros.
- Licensed for use within one organization.
- NIST SP 800-171/171A and FAR requirement text is quoted verbatim (public domain). Check your contract and the current rules for what applies to you.
- These templates help you prepare and document an honest self-assessment. They do not guarantee a particular SPRS score, a passing assessment or contract eligibility.
- 5-day fit guarantee: if it does not fit your system, contact us within 5 days of purchase.


What every download includes
Instant downloadLink on the confirmation page and by email within minutes.
Fully editableWord (.docx), Excel (.xlsx) and PDF. No macros. Works in Microsoft 365 and Google Workspace.
5-day fit guaranteeIf the files do not fit your CMMC program, ask for a refund within 5 days. Conditions apply.
Free updatesRevised files for the NIST SP 800-171 revision that CMMC enforces are sent to you at no charge. One-organization licence.
Built from the official NIST SP 800-171 Rev 2 and SP 800-171A text (US Government works). Templates help you prepare for a self-assessment or an assessment; they do not guarantee a passing score, a contract award or legal compliance.
Questions about NIST 800-171 System Security Plan (SSP) Template
What is a System Security Plan?
It is the document that describes your CUI environment, its boundary and connections, who is responsible for what, and how each of the 110 NIST SP 800-171 requirements is implemented. Requirement 3.12.4 requires it, and assessors use it as their map. Without an SSP, a self-assessment cannot be scored.
How long does it take to write an SSP?
The Start Here guide estimates one to three days for sections 1 to 3 and diagrams, then three to six weeks part time to draft the 110 requirement statements, plus a week of review. Starting with the example statements saves time, but every one must be rewritten to describe what you actually do.
Can we describe controls we plan to implement?
Not as if they are in place. Each requirement has a status box; mark it honestly and reference the POA&M item for anything not yet implemented. Describing planned controls as implemented is a common and serious mistake, because your SPRS score and affirmation rely on the SSP being accurate.
Does the SSP cover shared responsibility with cloud and IT providers?
Yes. There is a section for external service providers and shared responsibility, so you write down which requirements your cloud platform, MSP or other providers meet, and which remain yours. The CMMC Level 2 Compliance Toolkit adds a separate shared responsibility matrix covering all 110 requirements.
How will I receive the files?
A download button appears on the order confirmation page and the same link is emailed to you within a few minutes. Bundles arrive as one ZIP file.
Can I get a refund?
Yes. With our 5-day fit guarantee, if the files do not fit your CMMC compliance program you can ask for a full refund within 5 days of your order. It applies once per customer and organization, covers the whole product, and requires you to confirm you have deleted the files. We also refund non-delivery, defective files, wrong items and duplicate purchases within 30 days. Read the full refund policy.
Can I see the files before I buy?
Yes. The images above show real pages from the files, and the free CMMC Level 1 self-assessment checklist lets you check where you stand before you buy.
Can I use the templates with more than one company?
Each purchase is licensed to one organization. Consultants and groups need one licence per client or legal entity. See the licence agreement.
Templates that work with this one
Useful next steps for a CMMC and NIST SP 800-171 self-assessment.

