


SOC 2 Starter Bundle (Policies, Control Matrix, Risk & Vendor)
$199Regular price $237
Instant download. Editable files. One-organization licence. 5-day fit guarantee.
Couldn't load pickup availability
Not ready to buy? Get the free SOC 2 readiness checklist
5-day fit guarantee. If it does not fit your SOC 2 program, ask for a refund within 5 days. Conditions.
Everything for SOC 2 readiness and for running your controls afterward: 53 files, including 52 editable templates in nine folders. The four individual SOC 2 products cost $286 separately; the toolkit is $249, a saving of $37, and adds five folders of operating templates sold only here.
SaaS companies of roughly 10 to 200 people preparing for a first Type 1 and moving on to Type 2, and teams on a compliance platform who want complete, company-specific documents and operating templates.


Templates refer to Trust Services Criteria numbers (for example CC6.1) and describe them in our own words; they do not reproduce AICPA text. A SOC 2 report is issued by a licensed CPA firm. Templates help you prepare; they do not guarantee a clean report.
Folders 05 to 09: the incident response plan, six playbooks, incident log and tabletop kit; the BC/DR plan, business impact analysis and DR test report; change log, onboarding and offboarding checklists and access review; org chart, committee charter and minutes, awareness deck and quiz; and the compliance calendar.
It is a realistic target for a focused team starting with reasonable technical foundations, such as a modern cloud stack and some existing security practice. Larger gaps, fewer people or several optional categories take longer. The free SOC 2 readiness checklist gives a quick sense of where you start.
Auditors sample evidence from the whole period, so controls must run on schedule. The compliance calendar lists 120 recurring activities by month and 35 event-driven controls, and the operating templates produce the records auditors ask for: access reviews, change logs, incident records, committee minutes and training completion.
No. Using everything at once is a common mistake. Follow the 90-day path, which introduces files in a sensible order, and drop or mark N/A what does not fit your company. Auditors test what you claim, so a smaller set of controls you really run beats a larger set you do not.
A download button appears on the order confirmation page and the same link is emailed to you within a few minutes. Bundles arrive as one ZIP file.
Yes. With our 5-day fit guarantee, if the files do not fit your SOC 2 program you can ask for a full refund within 5 days of your order. It applies once per customer and organization, covers the whole product, and requires you to confirm you have deleted the files. We also refund non-delivery, defective files, wrong items and duplicate purchases within 30 days. Read the full refund policy.
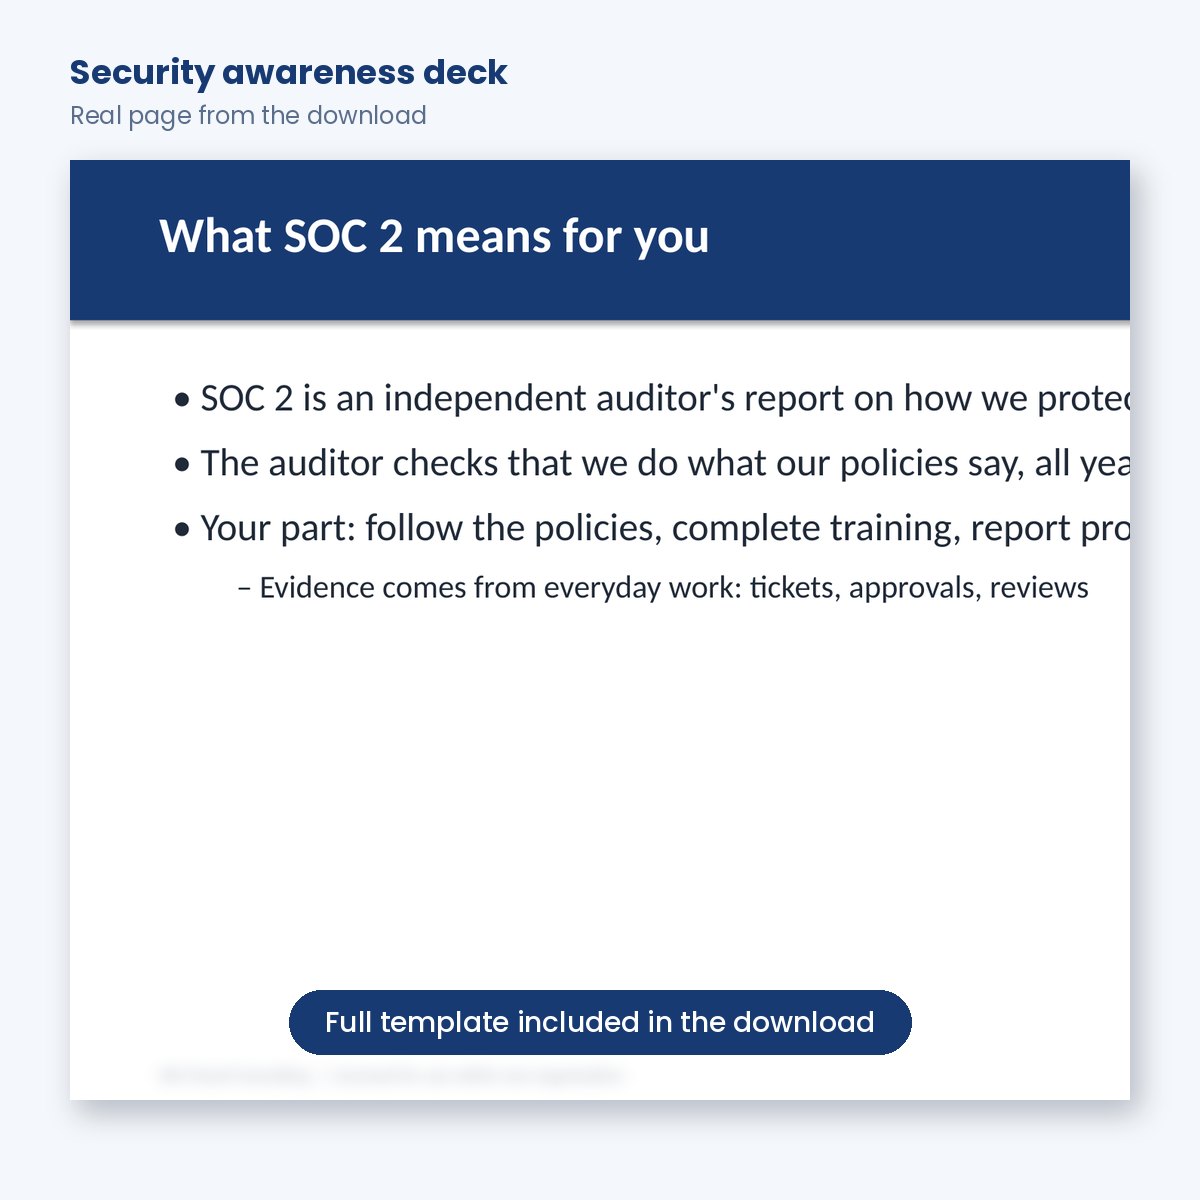
Yes. The images above show real pages from the files, and the free SOC 2 readiness checklist lets you check where you stand before you buy.
Each purchase is licensed to one organization. Consultants and groups need one licence per client or legal entity. See the licence agreement.
Useful next steps when you prepare for a SOC 2 audit.

