



SOC 2 Policy Templates Pack (20 Editable Policies)
SOC 2 Policy Templates Pack (20 Editable Policies)
Regular price
$129.00 USD
Regular price
Sale price
$129.00 USD
Instant download. Editable files. One-organization licence. 30-day money-back guarantee.
Couldn't load pickup availability
One-organization licence · Free updates for this edition · Email support· Purchase terms
- 30-day money-back guarantee. If it does not fit your SOC 2 program, email us within 30 days for a full refund. Conditions.
- Know what you are buying. The images above are real, unedited pages from the download, and a free sample is a few lines down.
- Secure checkout, instant access. Card, PayPal, Apple Pay, Google Pay or Shop Pay. Your download link is emailed to you within minutes of checkout, and you can re-download from your order confirmation at any time. Sold by ISO Cloud Consulting LLC, USA.
- Ask the author before you buy. Email a question and the person who wrote the files replies within 2 business days.
Upgrade and save
This is one of the 3 kits in the SOC 2 Starter Bundle: 20 policy templates, the readiness assessment and control matrix, and the risk assessment and vendor management kit. Get all 3 for $199 instead of $237 bought separately.
See the SOC 2 Starter Bundle (Policies, Control Matrix, Risk & Vendor)Want everything for the audit? The SOC 2 Compliance Toolkit has all 52 templates for $249.
Optional add-ons, training and free samples
Not ready to buy? Get the free SOC 2 readiness checklist
Before you buy
- Who wrote it: Ishan Maharaj, an industrial engineer (BSc Eng Hons, MSc Engineering Management) who builds and runs certified ISO 9001 and ISO 13485 quality systems. See the ISO 9001 and ISO 13485 case studies.
- Buying for a company? Need a quote or invoice for a purchase order first? Email hello@isocloudconsulting.com and we will send one.
- Not sure it fits? Email the same address with your company size and scope, and get a straight answer from the person who wrote the files.
Twenty editable SOC 2 security policies that read like your company, not a generic template. Each one is mapped to the Trust Services Criteria and ends with the evidence auditors usually request.
What you get
- 20 policies (Word, 105 pages in total): Information Security, Access Control, Acceptable Use, Asset Management, Change Management, Secure Software Development, Data Classification and Handling, Data Retention and Disposal, Encryption and Key Management, Incident Response, Business Continuity and Disaster Recovery, Backup, Vendor and Third-Party Management, Risk Management, Human Resources Security, Security Awareness and Training, Logging and Monitoring, Vulnerability and Patch Management, Network and Cloud Security, and Code of Conduct.
- Consistent structure in every policy: purpose, scope, roles, numbered policy statements, standards and minimums, exceptions, enforcement, review, related criteria and an evidence table, with blue Guidance notes and [square-bracket] placeholders.
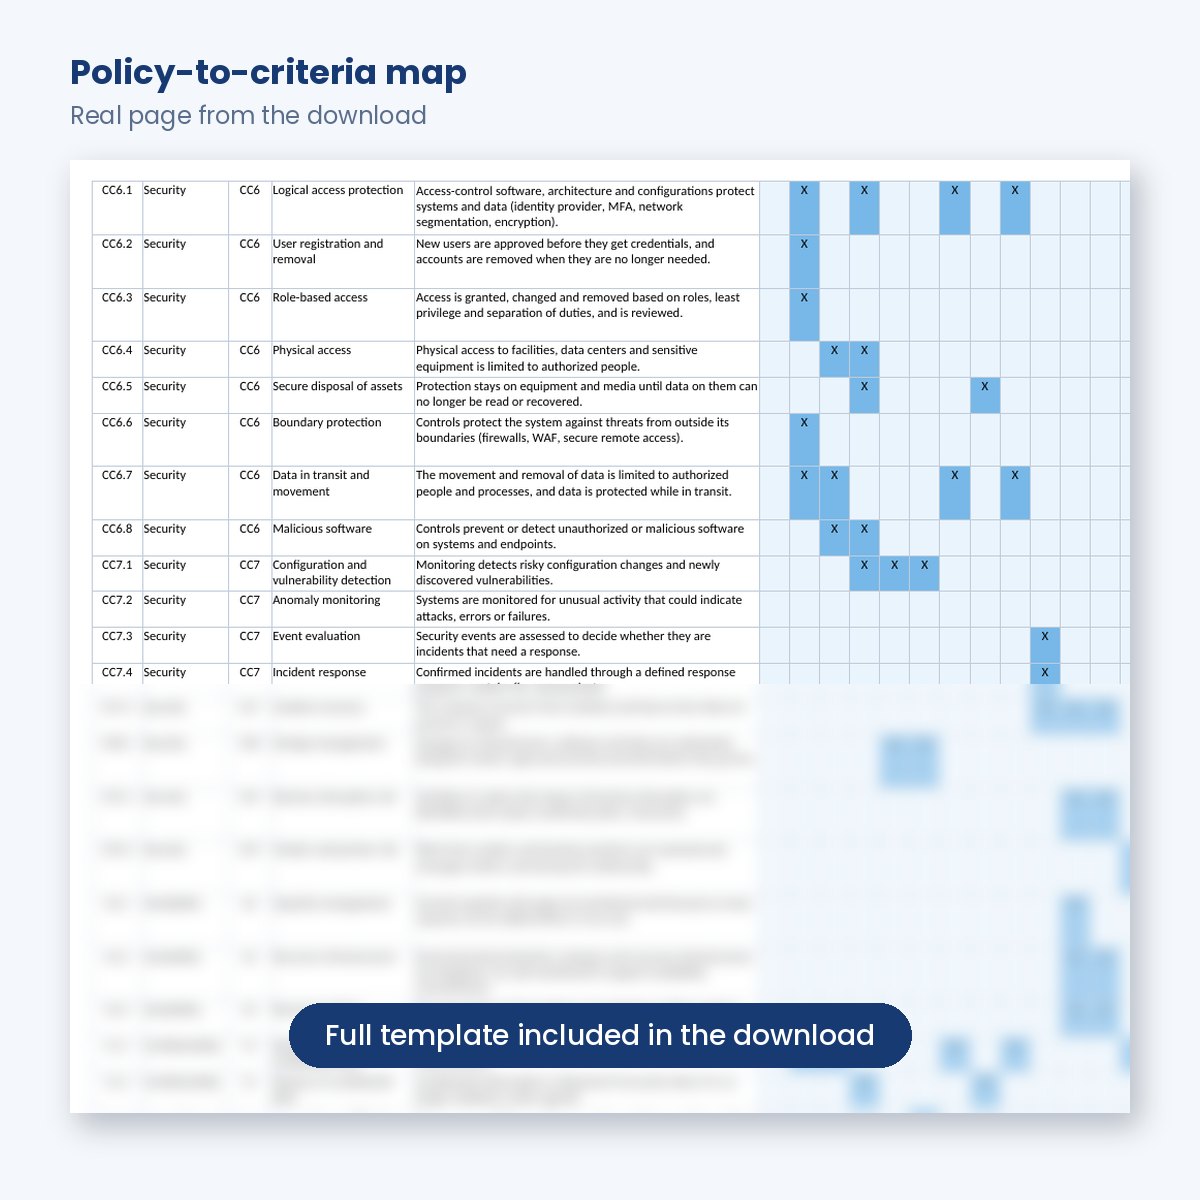
- Policy-to-Criteria Map (Excel): all 20 policies mapped to all 61 criteria, with an automatic coverage check.
- Acknowledgement and Review Tracker (Excel): policy approval and review register, staff acknowledgement tracker, review log and dashboard.
- Start Here guide (PDF, 4 pages): the order of work, default owners and common mistakes.
Also included in the SOC 2 Starter Bundle and the SOC 2 Compliance Toolkit.
How to use it
- Read policy 01 end to end; it sets the governance model the others rely on.
- Find and replace your organization name, product name, cloud and identity providers and role titles across all 20.
- Work through each policy with its owner, changing every bracketed number to one you will reliably meet.
- Check the coverage map, approve the policies and record dates in the tracker.
- Publish, run an acknowledgement campaign and collect evidence from day one.
Who it is for
Founders, CTOs, first security hires and operations leads at SaaS companies of roughly 10 to 200 people preparing for a first SOC 2 report, including teams on a compliance automation platform who want policies that match how they really work.
Good to know
- Instant download. Editable Word (.docx) and Excel (.xlsx), plus a PDF guide. Works in Excel 2016 or later, Microsoft 365 and LibreOffice; no macros.
- Licensed for use within one organization.
- Criteria are referenced by number and summarized in our own words; the AICPA criteria are free to download from the AICPA.
- SOC 2 is an attestation report by a licensed CPA firm, not a certification. These templates help you prepare; they do not guarantee an unqualified SOC 2 opinion.
- 30-day money-back guarantee: if it does not fit your system, contact us within 30 days of purchase.


SOC 2 Policy Templates Pack (20 Editable Policies)$12930-day money-back guarantee
What every download includes
Instant downloadLink on the confirmation page and by email within minutes.
Fully editableWord (.docx), Excel (.xlsx) and PDF. No macros. Works in Microsoft 365 and Google Workspace.
30-day money-back guaranteeIf the files do not fit your SOC 2 program, ask for a full refund within 30 days. Conditions apply.
Free updatesRevised files for the current version of the Trust Services Criteria are sent to you at no charge. We email you the new files. Version history.
Templates refer to Trust Services Criteria numbers (for example CC6.1) and describe them in our own words; they do not reproduce AICPA text. A SOC 2 report is issued by a licensed CPA firm. Templates help you prepare; they do not guarantee a clean report. Licence, updates and refunds in one place: purchase terms. Sold by ISO Cloud Consulting LLC.
Questions about SOC 2 Policy Templates Pack (20 Editable Policies)
Which policies does SOC 2 require?
The Trust Services Criteria do not publish a mandatory policy list, but auditors expect written, approved policies behind your controls. These 20 cover what a typical SaaS company is tested on for Security, with support for Availability, Confidentiality, Processing Integrity and Privacy. The Policy-to-Criteria Map shows which policy supports each criterion.
How much editing do the policies need?
Plan 20 to 40 minutes per policy with its owner, after a global find-and-replace of names and tools. The most important edit is changing every bracketed number, such as review frequencies and patching timelines, to a value you already meet. Auditors test what you wrote, so promises you cannot keep become exceptions.
Will these policies work with a compliance automation platform?
Yes. Many teams upload their own policies to a platform because the built-in ones read generically. Each file is a normal Word document, and the criteria references and evidence tables help you link policies to the platform's controls. Keep the tracker or use the platform's acknowledgement feature, whichever you prefer.
Do policies alone get us a SOC 2 report?
No. Policies set the rules; controls put them into practice; evidence proves the controls happened. An auditor reads the policies first, then tests whether what they say actually happens. You also need a control matrix, a risk assessment, vendor reviews and evidence, which the SOC 2 Starter Bundle adds.
How will I receive the files?
A download button appears on the order confirmation page and the same link is emailed to you within a few minutes. Bundles arrive as one ZIP file.
Can I get a refund?
Yes. With our 30-day money-back guarantee, if the files do not fit your SOC 2 program you can ask for a full refund within 30 days of your order. It applies once per customer and organization, covers the whole product, and requires you to confirm you have deleted the files. We also refund non-delivery, defective files, wrong items and duplicate purchases within 30 days. Read the full refund policy.
Can I see the files before I buy?
Yes. The images above show real pages from the files, and the free SOC 2 readiness checklist lets you check where you stand before you buy. You can also see a fully worked example of a procedure and its linked records.
Will I get updates?
Yes, for the current version of the Trust Services Criteria. Corrections and changes for that version are sent to you free, by email, for as long as we sell the product. If the criteria are replaced by a new version, the new kit is a separate product and existing buyers get an upgrade discount. See the version history.
Can I use the templates with more than one company?
Each purchase is licensed to one organization (one legal entity). Consultants can use one product with up to 10 client organizations with the Consultant Multi-Client Licence, including applying their own or the client's branding. See consultant rights and the licence agreement.

Who wrote these templates
Ishan Maharaj
Founder and Principal Consultant
BSc Engineering (Industrial) Honours and MSc Engineering Management
An industrial engineer who has worked in regulated medical device manufacturing throughout his career, in senior operations and quality leadership roles since 2019. Every template on this site was written and checked by him against the published standard, and the same person answers your questions.
Templates that work with this one
Useful next steps when you prepare for a SOC 2 audit.

